Overview
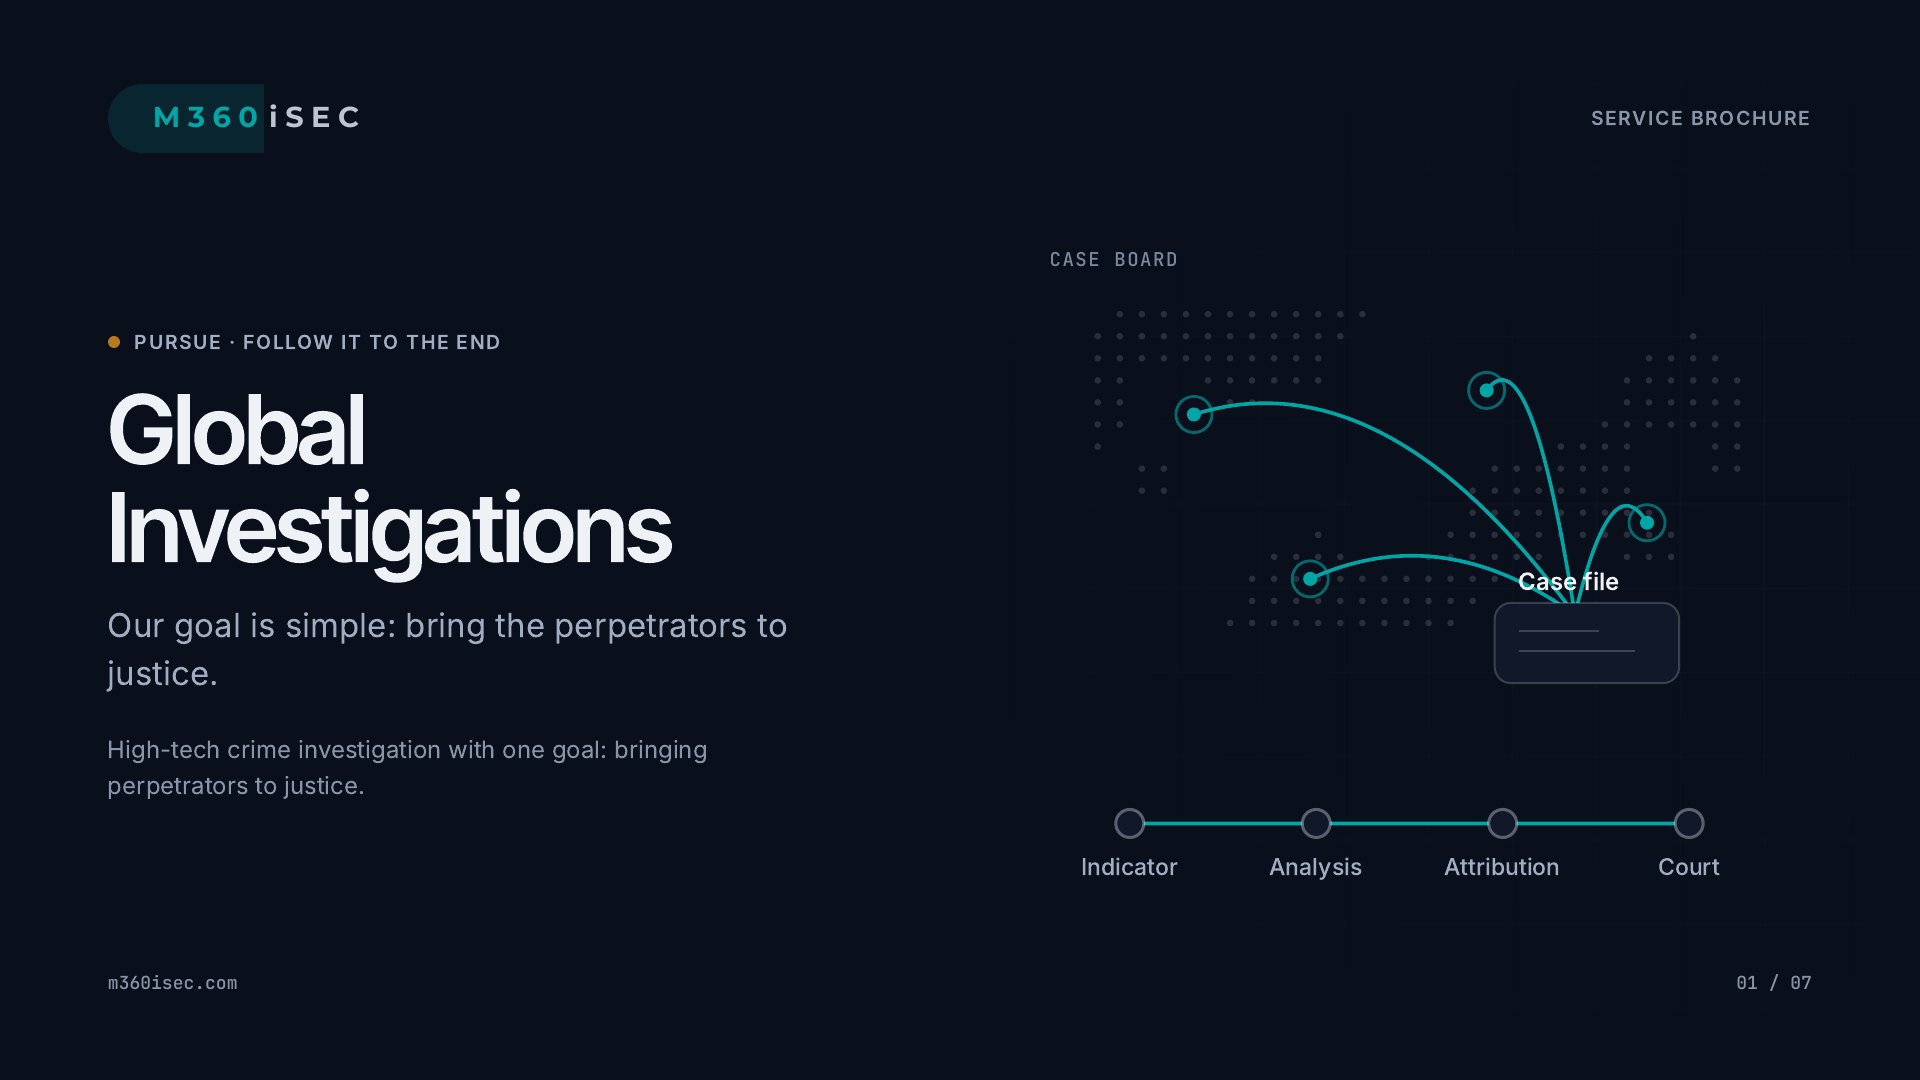
Our goal is simple: bring the perpetrators to justice.
High-tech crime investigation is our oldest practice. We build a detailed threat actor profile, dissect the anatomy of the attack and the attacker's infrastructure, and recreate the sequence of events.
When needed, we stay on the case until a sentence is carried out — working with your lawyers and providing testimony in court.
Scope
Global Investigations
- ✓Data theft
- ✓Financial crimes
- ✓Insider attacks
- ✓DoS / DDoS attacks
- ✓Critical infrastructure attacks
- ✓Malware attacks
Approach
How we work
- 01ScopeRules of engagement, allowed targets and knowledge levels agreed in writing.
- 02ReconnaissanceWe map your attack surface exactly as an outsider would see it.
- 03ExecutionThe same tactics and techniques as a real attacker: digital, physical and human.
- 04EvidenceEvery finding with proof, business impact and a prioritized fix.
- 05DebriefWe walk technical and executive teams through what we found and what to fix first.
What you receive
High-tech crime investigation with one goal: bringing perpetrators to justice.
- 01Expert forensic report
- 02Evidence with chain of custody
- 03Threat actor profile and timeline
- 04Legal support and court testimony
Why M360iSEC
A specialist practice, not a report factory.
- We think like the adversaryWe use the same tools, tactics and techniques as a real attacker to find what is actually exposed.
- From finding to courtroomIf prevention fails, the same team investigates, preserves evidence and supports the legal process.
- Certified specialistsProfessionals holding 75 certifications, including GIAC in digital forensics and malware analysis.
- Regional experienceBased in Bogotá, serving clients in 9 countries for over a decade.
- 75Certifications
- 12Specialists
- 30+Clients
- 9Countries served
Protect, Prevent & Pursue.
Let's talk
We will propose a written scope, with no commitment.
- sales@m360isec.com
- Website
- m360isec.com
- Office
- Carrera 56 #151-52, Torre 5 — Of. 101 · Bogotá, Colombia
24/7 incident response